The problem at the core
Handheld Android POS fleets create a deceptively simple promise — fast transactions, mobility, happier staff — that collapses into constant patching, unpredictable failures, and security gaps. This is a problem-driven piece: we start with what breaks and work back to practical fixes that teams can implement today. For teams facing regulatory pressure and persistent outages, integrating robust digital security solutions with lifecycle practices isn’t optional; it’s necessary. My approach draws on field experience managing deployments in retail and hospitality, and it is anchored by public incidents like the WannaCry disruption to the UK’s NHS in 2017, which exposed how neglected device maintenance ripples into service outages and reputational damage.
Why handheld Android POS fleets fragment
Fragmentation stems from competing vendor firmware versions, varied hardware models, and ad-hoc OTA updates. Add third-party apps and inconsistent endpoint management, and you have a brittle stack. Industry terms matter here: firmware mismatches and weak encryption increase attack surface; absent mobile device management (MDM) policies mean devices age in production without coordinated patching. The result: unpredictable failures and costly emergency fixes.
Operational teardown: where teams most often fail
Most operational failures are avoidable because they follow predictable patterns. Teams skip standardized images, trust factory defaults, or allow shadow IT to install unvetted software. The typical teardown reveals five recurring issues: missing device inventory, no secure boot enforcement, irregular update cadence, insufficient logging, and lack of certificate lifecycle control. And yes — supply-chain staging is often an afterthought, which amplifies risk during rollouts. This is where {main_keyword} and {variation_keyword} belong in a practical checklist rather than as marketing copy: embed them into the deployment scripts and manifests used during staging, so they’re versioned and auditable.
Concrete fixes that actually scale
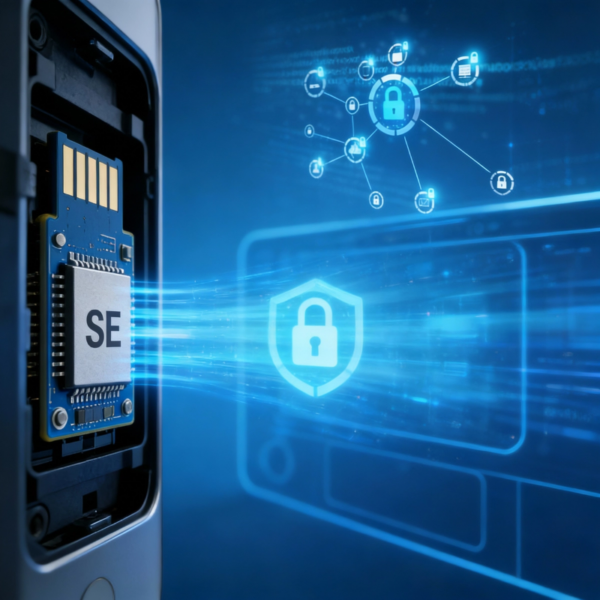
Start with a baseline image and treat each POS terminal as an endpoint requiring full lifecycle management. Implement these concrete steps: a strict mobile device management policy, automated OTA updates tested in a staging cluster, enforceable encryption and secure boot, and multi-factor authentication for admin access. Use zero-trust principles to isolate compromised devices quickly. For auditing and compliance, centralize logs and tie them to a change-control process. When you combine these controls with vendor-signed updates you reduce rollback incidents and accelerate recovery. For teams wanting hardening guidance that maps to production workflows, look for integrated digital security solution offerings that align device provisioning with update orchestration.
Common mistakes and how to avoid them
Teams often assume a single patch schedule fits all devices — that’s wrong. Different models require staggered testing and staged rollouts. Another misstep: trusting baseband or peripheral firmware without validation. — Run automated compatibility tests before mass updates. Also, don’t let operational ownership fall into a gap between IT and store ops; assign explicit lifecycle roles and KPIs so nobody assumes someone else will patch or replace failing hardware.
Lessons from real incidents
When major outages hit — think of the public chaos after widely reported infrastructure breaches — the root cause is rarely a sudden, mysterious flaw. It’s poor lifecycle hygiene: missing inventories, unpatched modules, and expired certificates. Those failures are data points proving that governance matters as much as technology. Practitioners who catalog devices, automate updates, and enforce secure boot see measurable drops in incident frequency and repair costs.
Three golden rules to evaluate any strategy
1) Measure coverage: percentage of devices under MDM and automated update control — aim for 98% or higher. 2) Test cadence: time from patch release to validated deployment in production — keep it under two weeks with staged rollouts. 3) Recovery maturity: mean time to remediate (MTTR) for device compromise — target single-digit hours, not days. These metrics give clear targets for procurement, engineering, and operations.
Practical device lifecycle work pays off in uptime, lower support costs, and stronger security posture — and that’s what BHDC brings into play as a cohesive partner for teams rebuilding their device foundations: BHDC. —