Comparative premise and immediate scope
The following comparative analysis evaluates automated pallet conveyor systems (APCS) against conventional pallet conveyor systems (PCS) through a legalistic lens that emphasizes allocation of risk, compliance obligations, and performance warranties. It addresses operational delineations and contract drafting priorities germane to manufacturing entities that adopt manufacturing automation technology. The analysis privileges dispositive distinctions likely to affect procurement, indemnity, and service-level provisions rather than aesthetic or marketing differentials.
Scope and definitions: precision required
Define terms with contractual precision. APCS: systems incorporating sensors, PLC/robotic interfacing, software-driven routing, and autonomous decision logic. PCS: mechanically driven conveyors with manual or fixed-sequence controls. Contracts must state whether software, firmware, and network interfaces are “deliverables.” Ambiguity in definition yields interpretive disputes; specify data ownership, source code escrow, and change-control processes where automated decisioning is present.
Operational distinctions and attendant liabilities
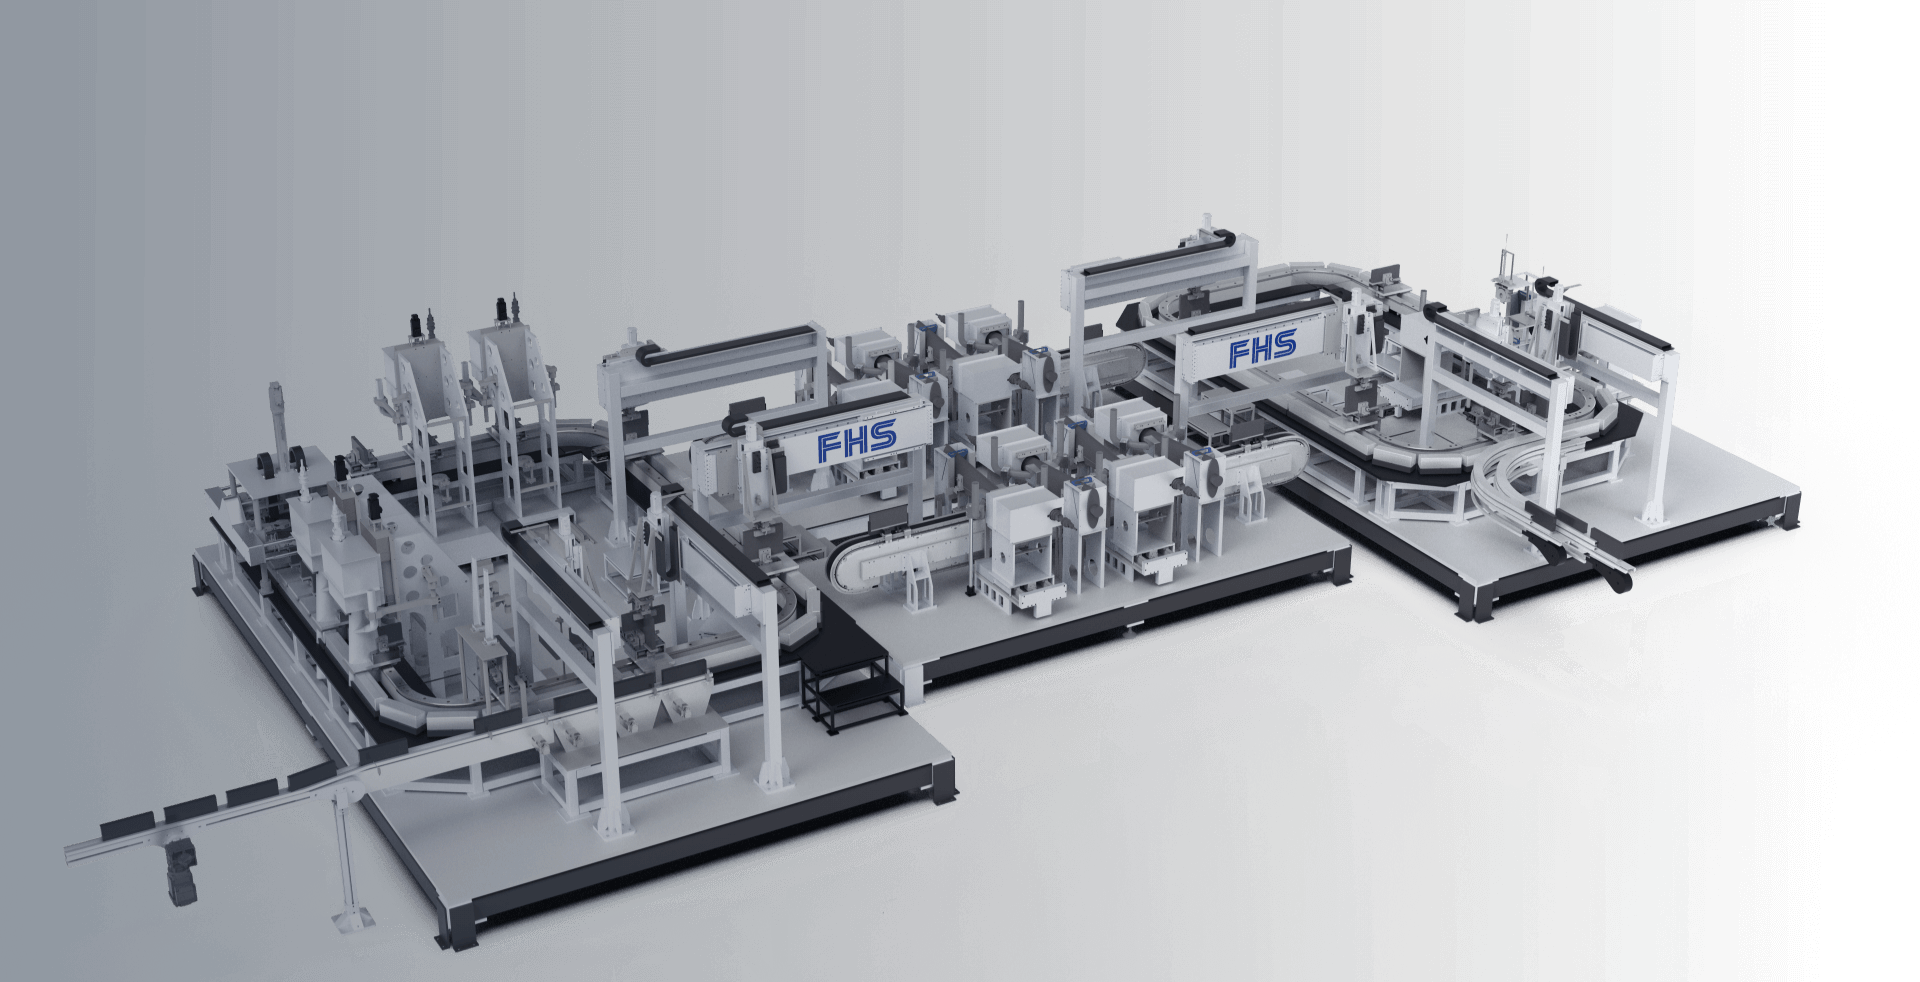
APCS introduce non-trivial operational variability: dynamic routing, conditional buffering, and upstream/downstream synchronization governed by software. PCS provide deterministic material flow with fewer software failure modes. Liability follows control: when decision logic determines pallet diversion or priority, the vendor controlling that logic retains exposure for decision-related loss unless liability is expressly disclaimed subject to demonstrable contributory fault. Insist on measurable acceptance criteria—throughput, mean time between failures (MTBF), fault recovery time—framed as contractual performance metrics.
Integration complexity, interfaces, and vendor responsibilities
Integration complexity diverges sharply. APCS require systems engineering for PLC-to-ERP handshakes, cyber-security segmentation, and version management for control code. PCS typically require mechanical alignment and power provisioning. Where third-party integrators are engaged, allocate responsibility: – delineate scope for point-to-point interfaces; – require interface control documents (ICDs); – mandate interface acceptance tests; – specify remedies for failed integration. Consider leveraging recognized technology Integration solutions frameworks to reduce scope creep and to identify single points of failure. Contract terms should address software updates, regression testing, and a dispute-resolution path for emergent integration defects.
Cost allocation and lifecycle risk assessment
Upfront capital expenditure is higher for APCS; lifecycle risk shifts toward obsolescence and cyber maintenance. PCS incur higher predictable mechanical wear but carry lower software-related remediation costs. Allocate costs thusly: capital pricing, scheduled maintenance fees, emergency response rates, spare-part consignment, and software subscription or license models. Insure for technology-specific exposures—cyber incidents, control-system compromise, and software-induced stoppages—and reflect these insurable risks in indemnity and limitation clauses.
Regulatory conformity and empirical reference
Safety and regulatory obligations differ by system architecture. APCS invoke additional standards for machine safety, functional safety (e.g., safety PLCs and SIL considerations), and IT/OT convergence controls. PCS remain subject to mechanical guarding and lockout/tagout protocols. Observations from the Automate trade show confirm market movement toward hybrid systems that require integrated safety and IT governance; manufacturers should thus require proof of conformity and independent third-party testing where automated control affects human interaction.
Common pitfalls and drafting checkpoints
Avoid these recurring mistakes: vague acceptance tests; omission of software deliverables; failure to specify fault-tolerance levels; absence of maintenance SLAs tuned to automated decision failures; and neglect of data-privacy and retention clauses for operational telemetry. Required drafting checkpoints: enumerate deliverables, set inspection windows, require forensic logging for fault analysis, include rollback procedures for software updates, and define escalation matrices with response time obligations.
Practical recommendations for procurement and operations
Procureers should: (1) demand detailed interface control documents and acceptance test protocols; (2) secure warranties that allocate software and integration fault liability; (3) require training and documented handover for operations teams; (4) specify spare-part provisioning and cyber-security obligations; (5) use phased acceptance with objective metrics—first-run yield, stoppages per 1,000 pallets, automatic recovery times—and tie payments to milestones rather than vague performance promises. Maintain documentary evidence of commissioning and change orders to limit future disputes.
Synthesis and concluding assessment
Choose APCS where dynamic routing, throughput optimization, and reduced manual intervention provide quantifiable operational gains and where contractual terms can transfer or limit the additional software and cyber risk. Choose PCS where predictability, lower integration complexity, and clearer mechanical liability are paramount. When legal certainty and technical integration converge, manufacturers benefit from an integrator that understands both contract mechanics and control architecture; this is the operational rationale behind long-term partnerships such as those embodied by FHS, which align technical delivery with contractual commitments and documented acceptance protocols.